Delegated access, governed
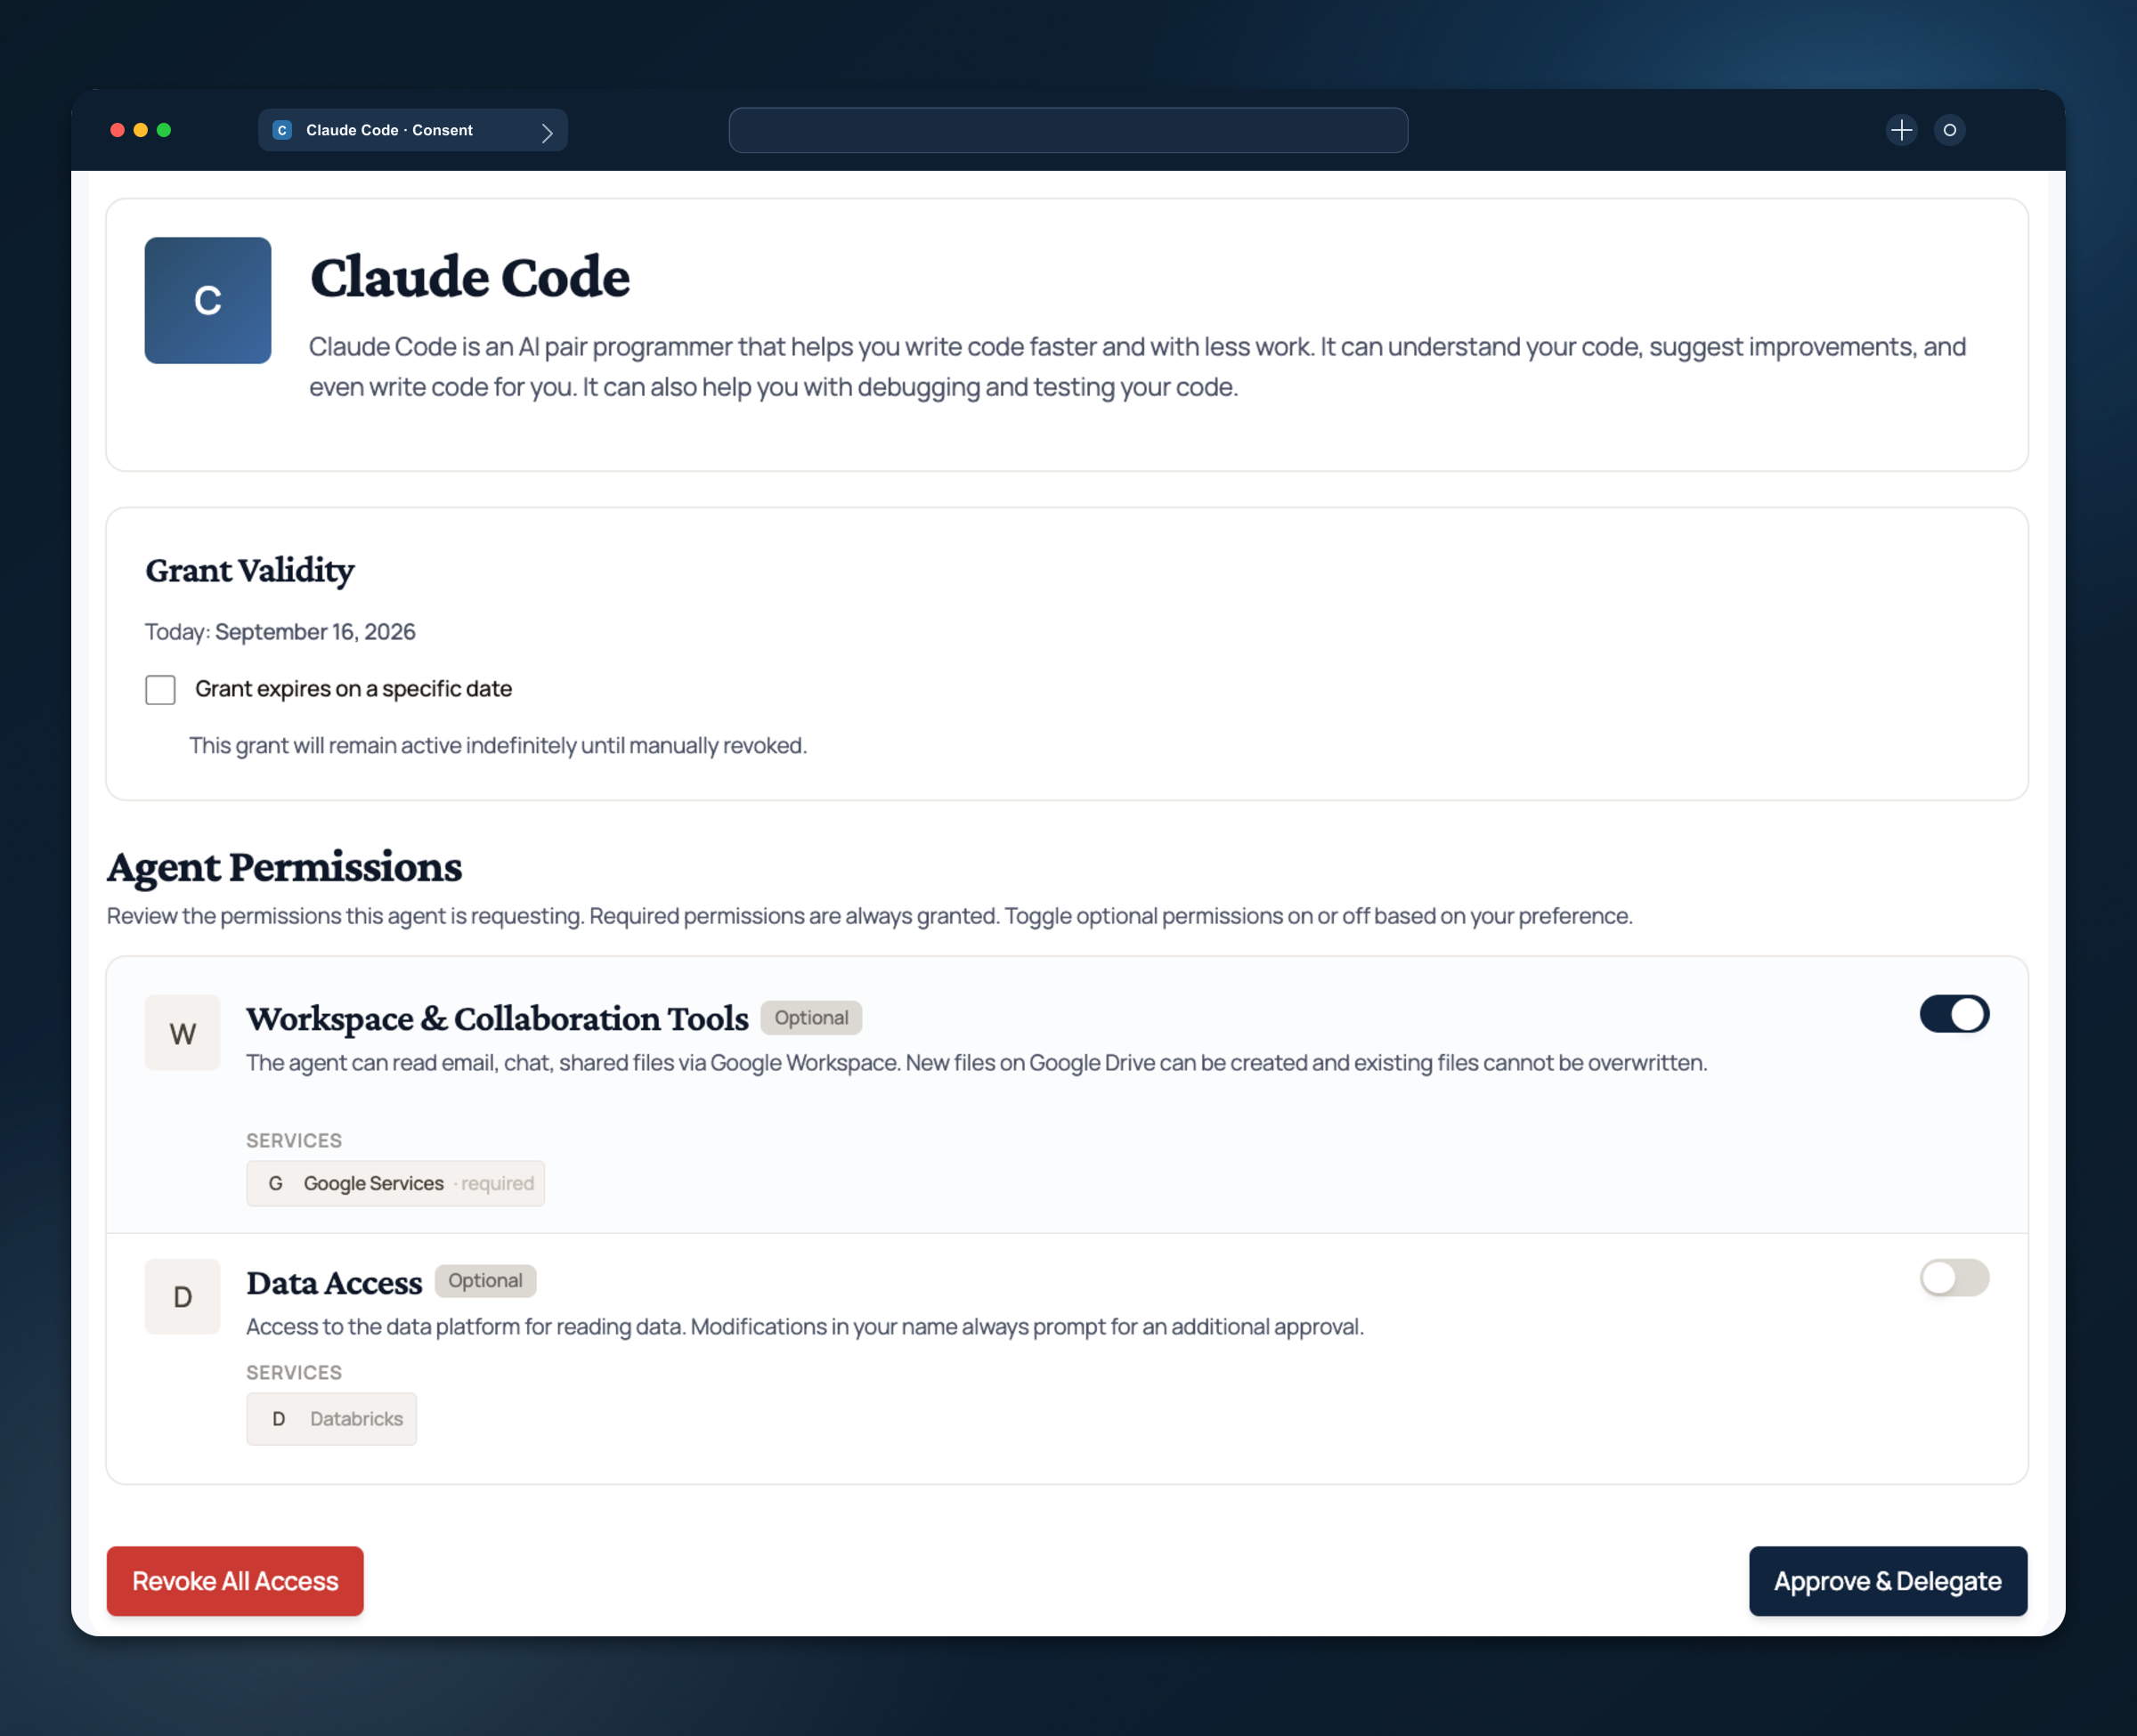
A user grants an agent access to specific third-party services at a chosen permission set, with optional expiry. One grant per user and agent, revocable at any time.
Governed delegated access for AI agents
The Agentic Identity Broker is a governed trust boundary between your users, the AI agents acting for them, and the third-party services those agents call. Users consent once per agent and service; the broker holds the third-party tokens encrypted and hands agents only narrowly-scoped, exchangeable, auditable access.
These docs focus on the concerns an IAM team or platform operator cares about: the delegation model, security posture, deployment, configuration, and the API contracts other systems integrate against.
A user grants an agent access to specific third-party services at a chosen permission set, with optional expiry. One grant per user and agent, revocable at any time.
The broker stores third-party access and refresh tokens encrypted at rest with envelope encryption bound to each service, so agents never hold long-lived provider credentials.
A gateway swaps an agent token for the right third-party token per request using RFC 8693, enforced by policy — transparently, with an optional Envoy sidecar.
What the broker is, the delegation problem it solves, and when to reach for it.
Open sectionConceptsThe delegation model, architecture, server modes, token exchange, and encryption.
Open sectionGet startedRun the full stack locally and walk a delegation from consent to token exchange.
Open sectionAPI referenceThe end-user and admin OpenAPI contracts, rendered from the source specifications.
Open section